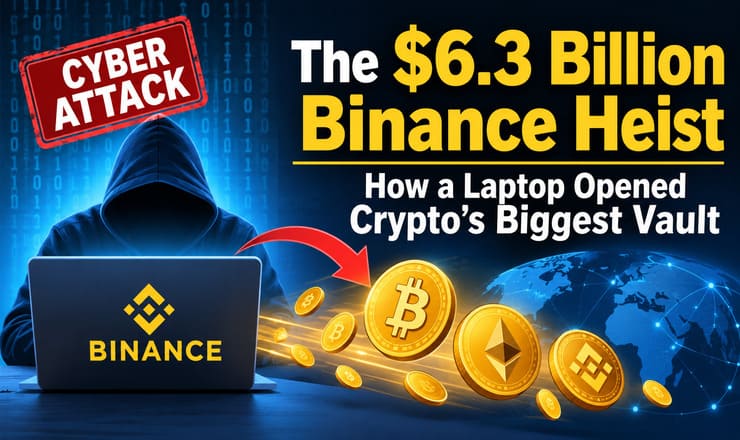
The world’s largest cryptocurrency exchange, Binance, suffered an unprecedented cyberattack on October 29, 2026, resulting in the theft of approximately $6.3 billion in cryptocurrency. What makes the incident particularly alarming is that the attack reportedly began with a compromised employee laptop, exposing weaknesses in the systems that authorize billions of dollars in digital asset transactions.
How Did the Hack Happen?
According to Binance’s initial investigation, attackers gained access to the company’s internal network through a compromised DevOps engineer’s laptop. This reportedly allowed them to access a service container and submit unauthorized withdrawal transactions.
However, the investigation later uncovered additional points of breach, suggesting that the attack was more complex than a single compromised device.
Blockchain security firms believe the attackers compromised Binance’s transaction-signing infrastructure. This system authorizes cryptocurrency transfers from exchange wallets. By manipulating this process, the attackers were able to drain funds from multiple wallets across several blockchain networks.
The bulk of the theft reportedly took place within approximately 20 minutes.
Who Was Behind the Attack?
Blockchain intelligence firms, including TRM Labs and Chainalysis, have linked the attack with high confidence to TraderTraitor, a hacking group associated with North Korea.
Investigators identified similarities with previous cyberattacks attributed to North Korean hackers, including the use of advance preparations, automated transactions and techniques to disguise the movement of stolen funds.
However, attribution remains based on cybersecurity and blockchain analysis.
What Happened to the Stolen Cryptocurrency?
Following the attack, cryptocurrency companies and stablecoin issuers, including Tether and Circle, moved to freeze assets that could still be controlled.
Approximately $2.8–$3 billion of the stolen cryptocurrency was initially reported as frozen. Other assets, particularly Bitcoin and Ethereum, were harder to freeze because their networks do not have a central authority capable of reversing transactions.
Binance stated that it would cover the losses using its Secure Asset Fund for Users (SAFU) and company resources.
As of November 1, Binance reported that it had recovered or arranged to cover approximately 95% of the stolen funds and planned to resume cryptocurrency withdrawals in phases.
Lessons for the Cryptocurrency Industry
The Binance incident highlights a critical cybersecurity lesson: protecting private keys alone is not enough. Employee devices, internal networks, transaction approval systems and access permissions can all become entry points for attackers.
Even sophisticated blockchain platforms remain vulnerable when the systems controlling them are compromised.
For cryptocurrency investors, the incident is also a reminder that holding digital assets on an exchange involves risks beyond market volatility. Exchange security, custody arrangements and transparency deserve careful consideration.